Multi Cloud Landing Zone
Aaron Echosit
Published
Multicloud Landing Zone
A production-grade, multicloud landing zone for AWS, Azure, and GCP — built with Terraform (IaC), Python (automation/account-vending/compliance), Go (policy engine CLI), OPA (policy-as-code), and GitHub Actions (CI/CD).
Why this exists
A landing zone is the foundational environment a organization stands up before any workload is deployed: account/subscription/project structure, network topology, identity & access baselines, guardrails, logging/audit trails, and the automation to provision it all repeatably and safely.
This repo gives you:
Org-level scaffolding — AWS Organizations OUs, Azure Management Groups, GCP Folders
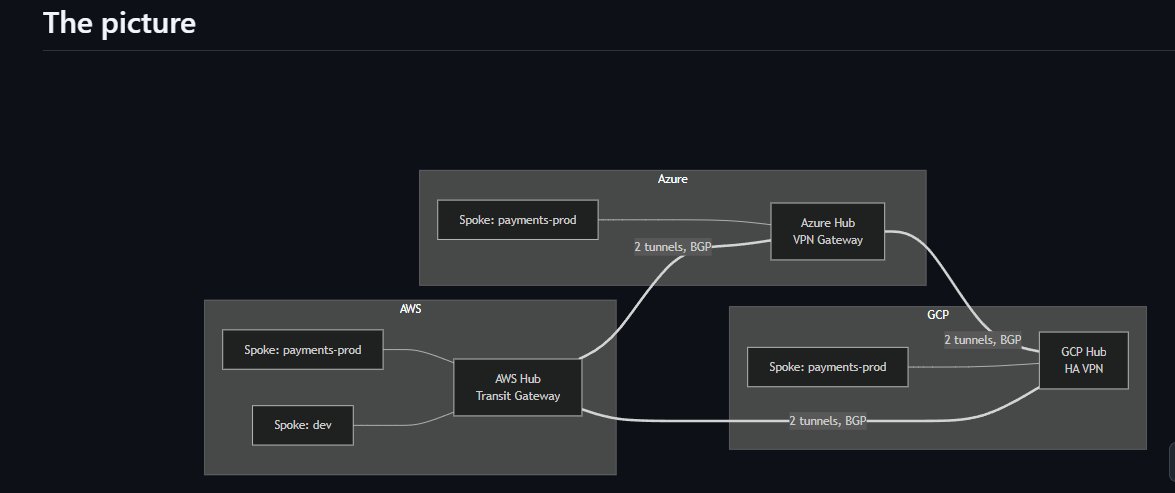
Hub-and-spoke networking per cloud, ready to peer/connect via Transit Gateway / Virtual WAN / Network Connectivity Center
Identity baselines — least-privilege IAM/RBAC roles, break-glass access, SCPs/ Azure Policy/Org Policies
Policy-as-code guardrails enforced in CI via OPA (Conftest) before any apply
Account/subscription/project vending via a Python CLI so new business units can self-serve a compliant environment
A Go policy-engine CLI that validates Terraform plans against the same guardrails used in CI, runnable locally or in pipelines
GitHub Actions pipelines with OIDC (no long-lived cloud credentials), plan/apply gating, and drift detection